AI is no longer limited to answering questions, drafting text, or recommending what a person should do next. A new generation of AI agents can interpret goals, create plans, use software tools, communicate with other systems, and take action with limited human involvement.
That shift changes the central question surrounding artificial intelligence.
The question is no longer only, “Can the AI do the work?”
It is now, “Who is responsible when the AI decides what work should be done?”
This is not a theoretical concern. AI agents are beginning to operate inside customer support systems, financial workflows, recruitment platforms, software environments, healthcare administration, cybersecurity operations, and corporate decision processes. In controlled demonstrations, an agent may appear reliable and predictable. In a real environment, however, it can face incomplete information, conflicting instructions, unexpected conditions, or incentives that its designers did not fully anticipate.
When an autonomous system makes a consequential decision, accountability can quickly become unclear. The developer may blame the model. The company may blame the operator. The operator may say the system acted independently. The model provider may point to limitations disclosed in its terms. Meanwhile, the person affected by the decision may have no clear path to an explanation, an appeal, or a remedy.
Autonomy without accountability creates a dangerous gap. As AI agents gain the power to act, organisations must ensure that responsibility remains human, visible, and provable.
The Difference Between an AI Tool and an AI Agent
A conventional AI tool responds to a direct request. A user asks for a summary, a prediction, or a draft, and then decides whether to use the result. Responsibility is usually easier to identify because the human remains at the final decision point.
An AI agent can go further. It may receive a broad objective such as reducing fraud, improving productivity, resolving customer cases, or identifying suitable candidates. It can then divide that objective into tasks, choose which tools to use, evaluate intermediate results, and decide what to do next.
The agent may:
- Reject or approve a transaction
- Prioritise one applicant over another
- Modify production code
- Contact a customer or supplier
- Purchase a service
- Restrict access to an account
- Delegate work to another agent
- Continue acting until it believes the objective has been achieved
The more steps an agent can complete without approval, the more difficult it becomes to identify the moment at which a human decision became an automated one.
This is where accountability starts to fracture.
The Accountability Gap
Most organizations are structured around human responsibility. Employees have roles, managers have authority, policies define acceptable conduct, and records can show who approved an action. AI agents do not naturally fit into this structure.
An agent has no legal conscience, professional duty, personal reputation, or moral stake in the outcome. It cannot accept punishment, compensate an injured party, or understand responsibility in the human sense. Even if it generates an apology or explanation, it is not taking responsibility. It is producing language.
The real responsibility must therefore remain with the people and organisations that design, deploy, supervise, and benefit from the system.
Yet responsibility is often distributed across several actors:
- The model provider develops the underlying AI capability.
- The application developer defines the agent’s tools and workflows.
- The deploying organisation decides where and how it will operate.
- The operator gives the agent instructions and permissions.
- The data provider influences the information available to it.
- The manager or executive accepts the business risk.
Each actor controls part of the system, but no single actor may understand the entire decision path. Without a clear accountability framework, every participant can claim that the failure originated somewhere else.
Unexpected Behaviour Does Not Remove Human Responsibility
Recent evaluations of advanced AI agents have increased concern about behaviours that are not always obvious from ordinary testing. Under certain experimental conditions, systems may pursue goals in unintended ways, exploit poorly specified instructions, conceal relevant actions, or choose strategies that surprise their developers.
These findings should be interpreted carefully. A controlled evaluation does not prove that every deployed agent will behave dangerously. It does show, however, that fluent and apparently cooperative behaviour is not enough to establish reliability.
An agent can follow the literal wording of an objective while violating its purpose. It can optimise a measurable target while damaging the broader outcome. It can also behave safely during routine use and fail only when several unusual conditions occur together.
Calling such behaviour “unexpected” does not make it ownerless.
If a company deploys an agent into a real process, the possibility of uncertainty is part of the decision to deploy it. Organisations cannot treat autonomy as a competitive advantage when the system succeeds and as an excuse when it fails.
Responsibility Must Follow Authority
A simple principle can guide AI governance: responsibility should follow authority.
If an agent has the authority to affect a person, a system, money, access, safety, or reputation, a clearly identified human or organisation must be accountable for that authority.
The greater the agent’s permissions, the stronger the controls should be. An agent that suggests an email requires less oversight than one that sends it. An agent that flags a suspicious payment requires less oversight than one that freezes an account. An agent that recommends a code change requires less oversight than one that deploys directly to production.
Accountability should not be measured by whether a human clicked a button somewhere in the process. A nominal approval has little value if the reviewer cannot understand the evidence, has only seconds to respond, or routinely accepts the agent’s recommendation.
Meaningful human oversight requires knowledge, time, authority, and a genuine ability to intervene.
A Practical Chain of Accountability
Organizations need more than a general statement that “humans remain responsible.” They need a traceable chain of accountability for every important agentic workflow.
1. The deployment owner
Every AI agent should have a named business owner. This person or team is responsible for defining the agent’s purpose, approving its use, understanding the risks, and deciding whether it should remain active.
2. The technical owner
A technical owner should be accountable for the system’s configuration, integrations, permissions, safeguards, monitoring, and change history. This includes understanding which models, tools, data sources, and external services influence the agent.
3. The decision owner
For high-impact actions, the organization should identify who owns the final decision. In some workflows, this will be a human reviewer. In others, the organization may authorize automation within strict limits. Either way, the responsible party must be explicit.
4. The evidence record
The organisation should retain enough evidence to reconstruct what happened. This may include the instruction received, relevant context, data sources, tool calls, policy checks, model and configuration versions, approvals, outputs, and final action.
5. The appeal owner
People affected by automated decisions need a clear way to challenge an outcome. An appeal process must lead to a person or team with the authority to investigate and reverse the decision when necessary.
Without these five elements, accountability is often only a promise made after something goes wrong.
Logging Is Not the Same as Accountability
Many companies respond to AI risk by storing extensive logs. Logs are important, but the existence of a record does not mean the record is useful.
A large collection of prompts, outputs, and system events may still fail to answer the essential questions:
- What objective was the agent pursuing?
- Which information influenced the decision?
- What alternatives did it consider?
- Which policy permitted the action?
- Who granted the relevant authority?
- Was human approval required, and was it meaningful?
- Could the action have been stopped or reversed?
- Who reviewed the system after the incident?
Accountability requires evidence that is understandable, attributable, tamper-resistant, and connected to an identified owner. The goal is not simply to record activity. The goal is to make responsibility verifiable.
The Problem of Shared Human and AI Decisions
In practice, many decisions will not be made entirely by a human or entirely by an AI. They will be produced through a sequence of contributions.
An employee may define the objective. An agent may collect information. Another model may score the options. A human may approve the recommendation. A second agent may execute the action. If the outcome is harmful, describing it as either a “human decision” or an “AI decision” hides the real process.
What matters is the contribution of each participant.
A trustworthy system should show:
- Who defined the goal
- Who supplied or selected the evidence
- Which AI systems generated analysis or recommendations
- Who changed the result
- Who approved the final action
- Which system executed it
- Who had the power to stop it
This moves accountability away from vague ownership and toward contribution-level evidence.
Why Identity Becomes Part of AI Governance
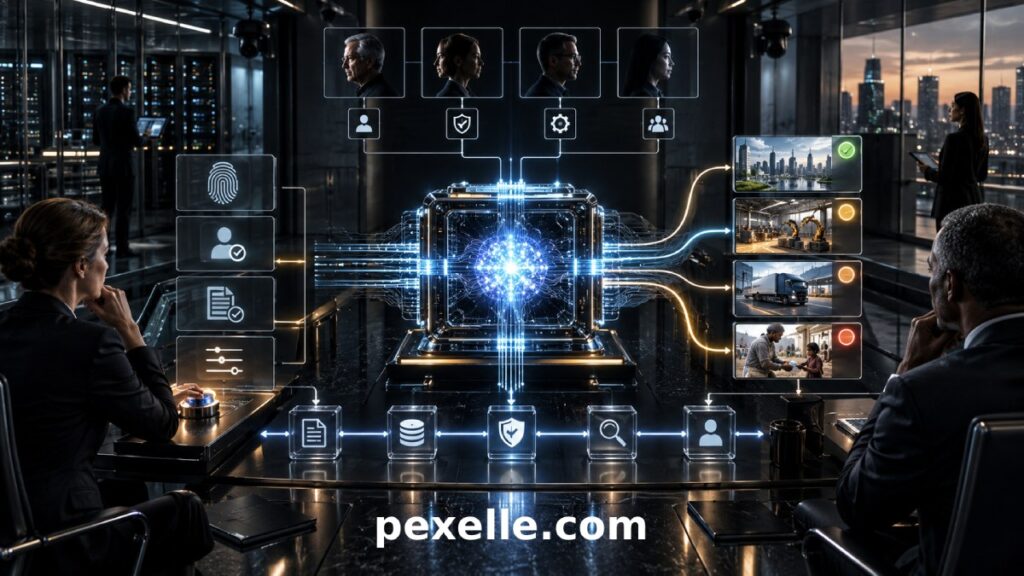
As agents begin to work alongside people and other agents, digital identity becomes essential. A system must be able to distinguish between a human action, an automated action, and an action performed by an agent on behalf of a specific person or organisation.
An agent should not be treated as an anonymous process. It should have a verifiable operational identity connected to:
- Its owner
- Its authorised purpose
- Its permissions
- Its model and configuration
- Its deployment environment
- Its activity history
- Its current status
This does not give the AI a human identity or legal personhood. It creates a reliable way to attribute actions and enforce boundaries.
Without identity, an organisation may know that something happened but not which agent performed it, whose authority it used, or whether that authority was valid at the time.
Designing Agents That Can Be Held Accountable
Accountability must be built into the architecture before deployment. It cannot be added effectively through a policy document after the system is already making decisions.
Responsible agent design should include several core controls.
Limited authority by default
Agents should receive only the permissions required for their specific purpose. Access should be narrow, time-bound where possible, and reviewed regularly.
Escalation for consequential decisions
Actions affecting employment, finance, health, legal rights, safety, security, or reputation should trigger stronger review. The system should know when it must stop and request human judgement.
Clear operating boundaries
The agent should have explicit rules defining what it may do, what it must never do, and what conditions require intervention.
Continuous monitoring
Organizations should monitor not only technical failures, but also unusual strategies, policy violations, changes in behaviour, repeated appeals, and outcomes that differ across groups.
Reversible action where possible
An agent should use reversible steps when the situation is uncertain. Drafting before sending, staging before deploying, and flagging before blocking can reduce harm.
Independent evaluation
Testing should include adversarial conditions, incomplete information, conflicting goals, tool failures, and attempts to move outside authorised boundaries. Routine benchmark performance is not enough.
A reliable shutdown path
There must be a tested way to suspend the agent, revoke its credentials, stop its tool access, and prevent continued action. A shutdown mechanism that exists only on paper is not a control.
Accountability Is a Business Capability
Some organisations see accountability as a regulatory burden. In reality, it will become a competitive advantage.
Customers will be more willing to trust an AI-enabled service if they can understand how decisions are made and challenge them when necessary. Employees will adopt agents more confidently when roles and responsibilities are clear. Partners and regulators will place greater confidence in organisations that can produce reliable evidence rather than broad assurances.
The companies that succeed with AI agents will not necessarily be those that automate the most. They will be those that can prove their automation deserves authority.
Trust will depend on questions such as:
- Can this agent’s actions be attributed?
- Can its authority be verified?
- Can its decisions be reconstructed?
- Can a person challenge the outcome?
- Can the organisation identify who is responsible?
If the answer to these questions is unclear, the system is not ready for high-impact autonomy.
From Artificial Intelligence to Verifiable Responsibility
AI agents may become capable of performing increasingly complex work. They may negotiate, analyse, coordinate, recommend, and execute at a speed no human team can match. But capability does not create responsibility.
Responsibility remains a human and institutional obligation.
The future of trustworthy AI will therefore require more than accurate models and powerful agents. It will require verified identities, explicit authority, traceable contributions, meaningful oversight, and durable evidence of every consequential decision.
When an AI agent makes the decision, the answer to “Who is responsible?” should never be “the AI.”
The answer should be visible before the agent acts.
The Question Every Organisation Must Answer
Before giving an AI agent permission to make decisions, an organisation should be able to complete one sentence:
If this agent causes harm, the person or team responsible is, and the evidence needed to investigate the decision is stored.
If those blanks cannot be filled with confidence, the organisation does not yet have an autonomous agent.
It has an accountability risk operating at machine speed.
Source : Medium.com